Exegol Workstation
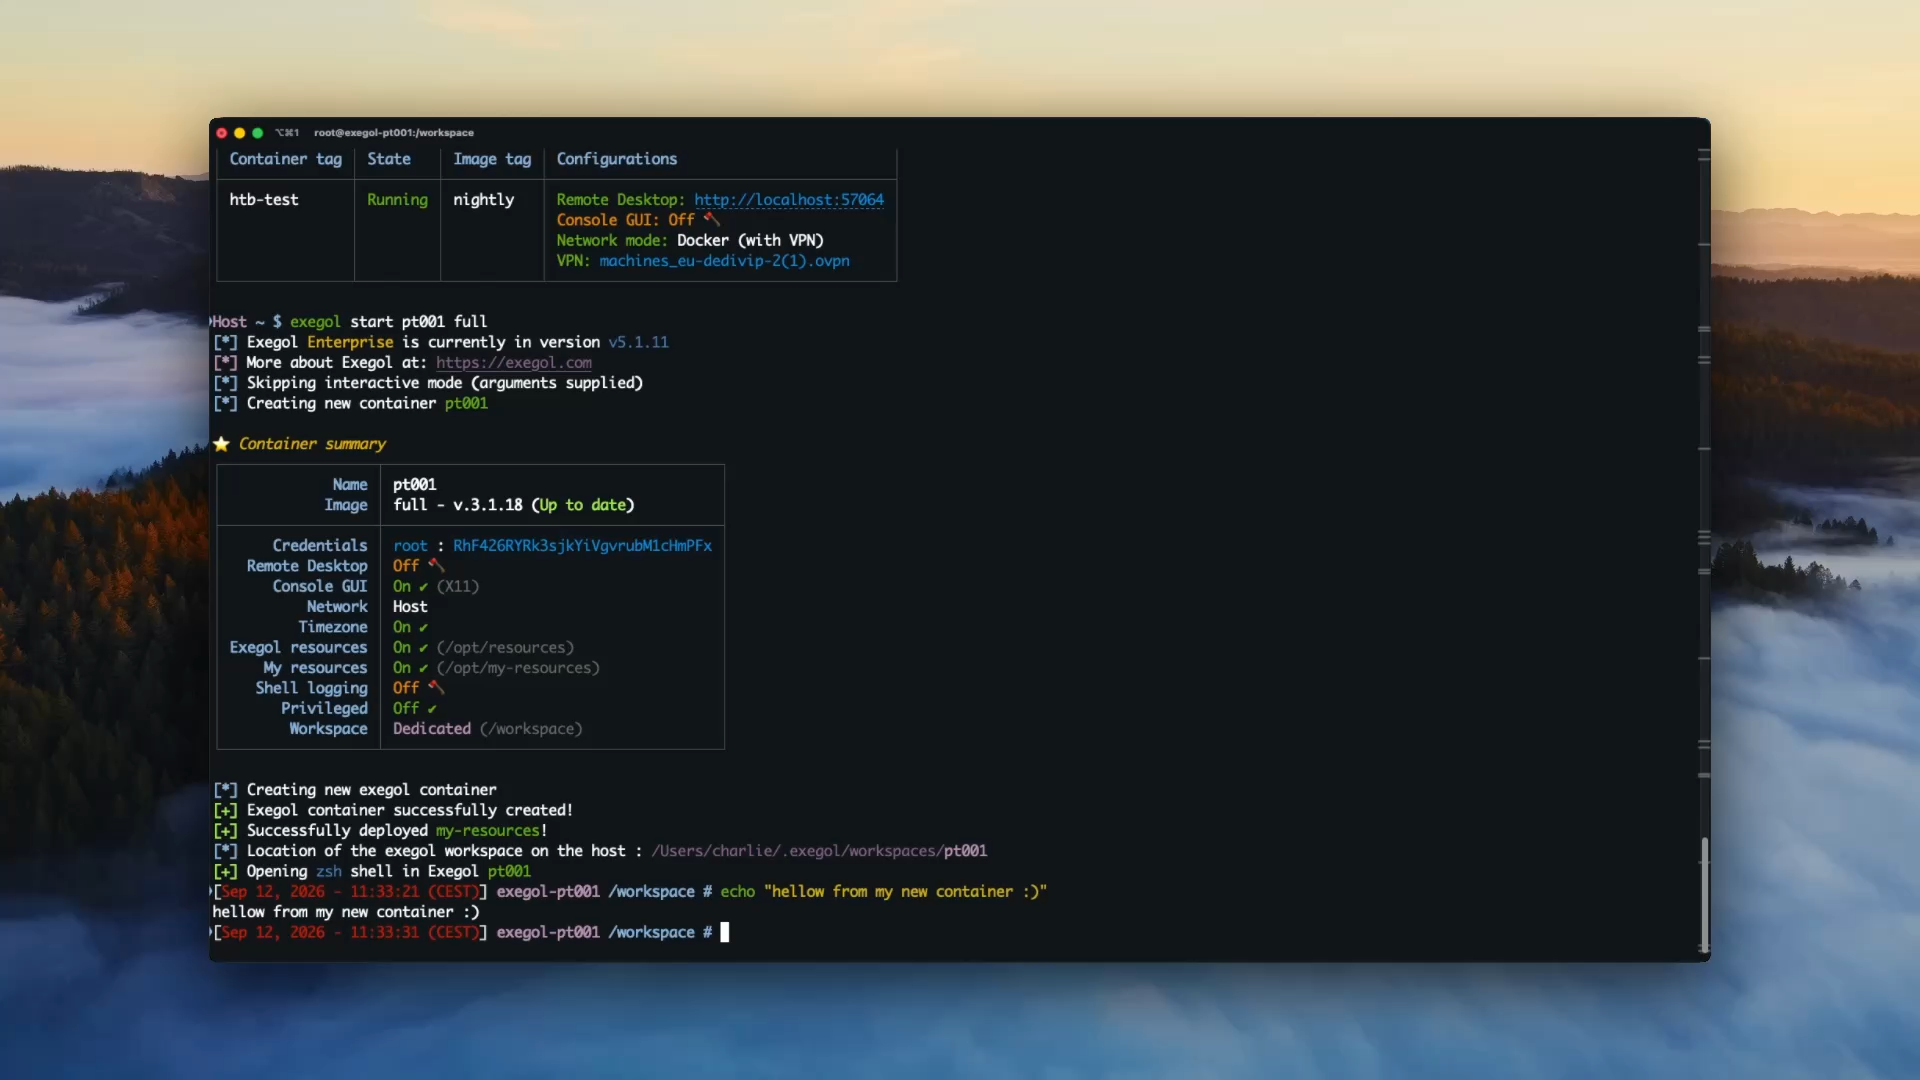
Offensive lab in Docker. Start a clean box per job. Not another distro. A maintained environment that Studio, MCP, and Sentinel plug into.
Containerized hacking environments for red teamers, testers, hunters, players. Lightweight, fast, empowering.
Offensive lab in Docker. Start a clean box per job. Not another distro. A maintained environment that Studio, MCP, and Sentinel plug into.
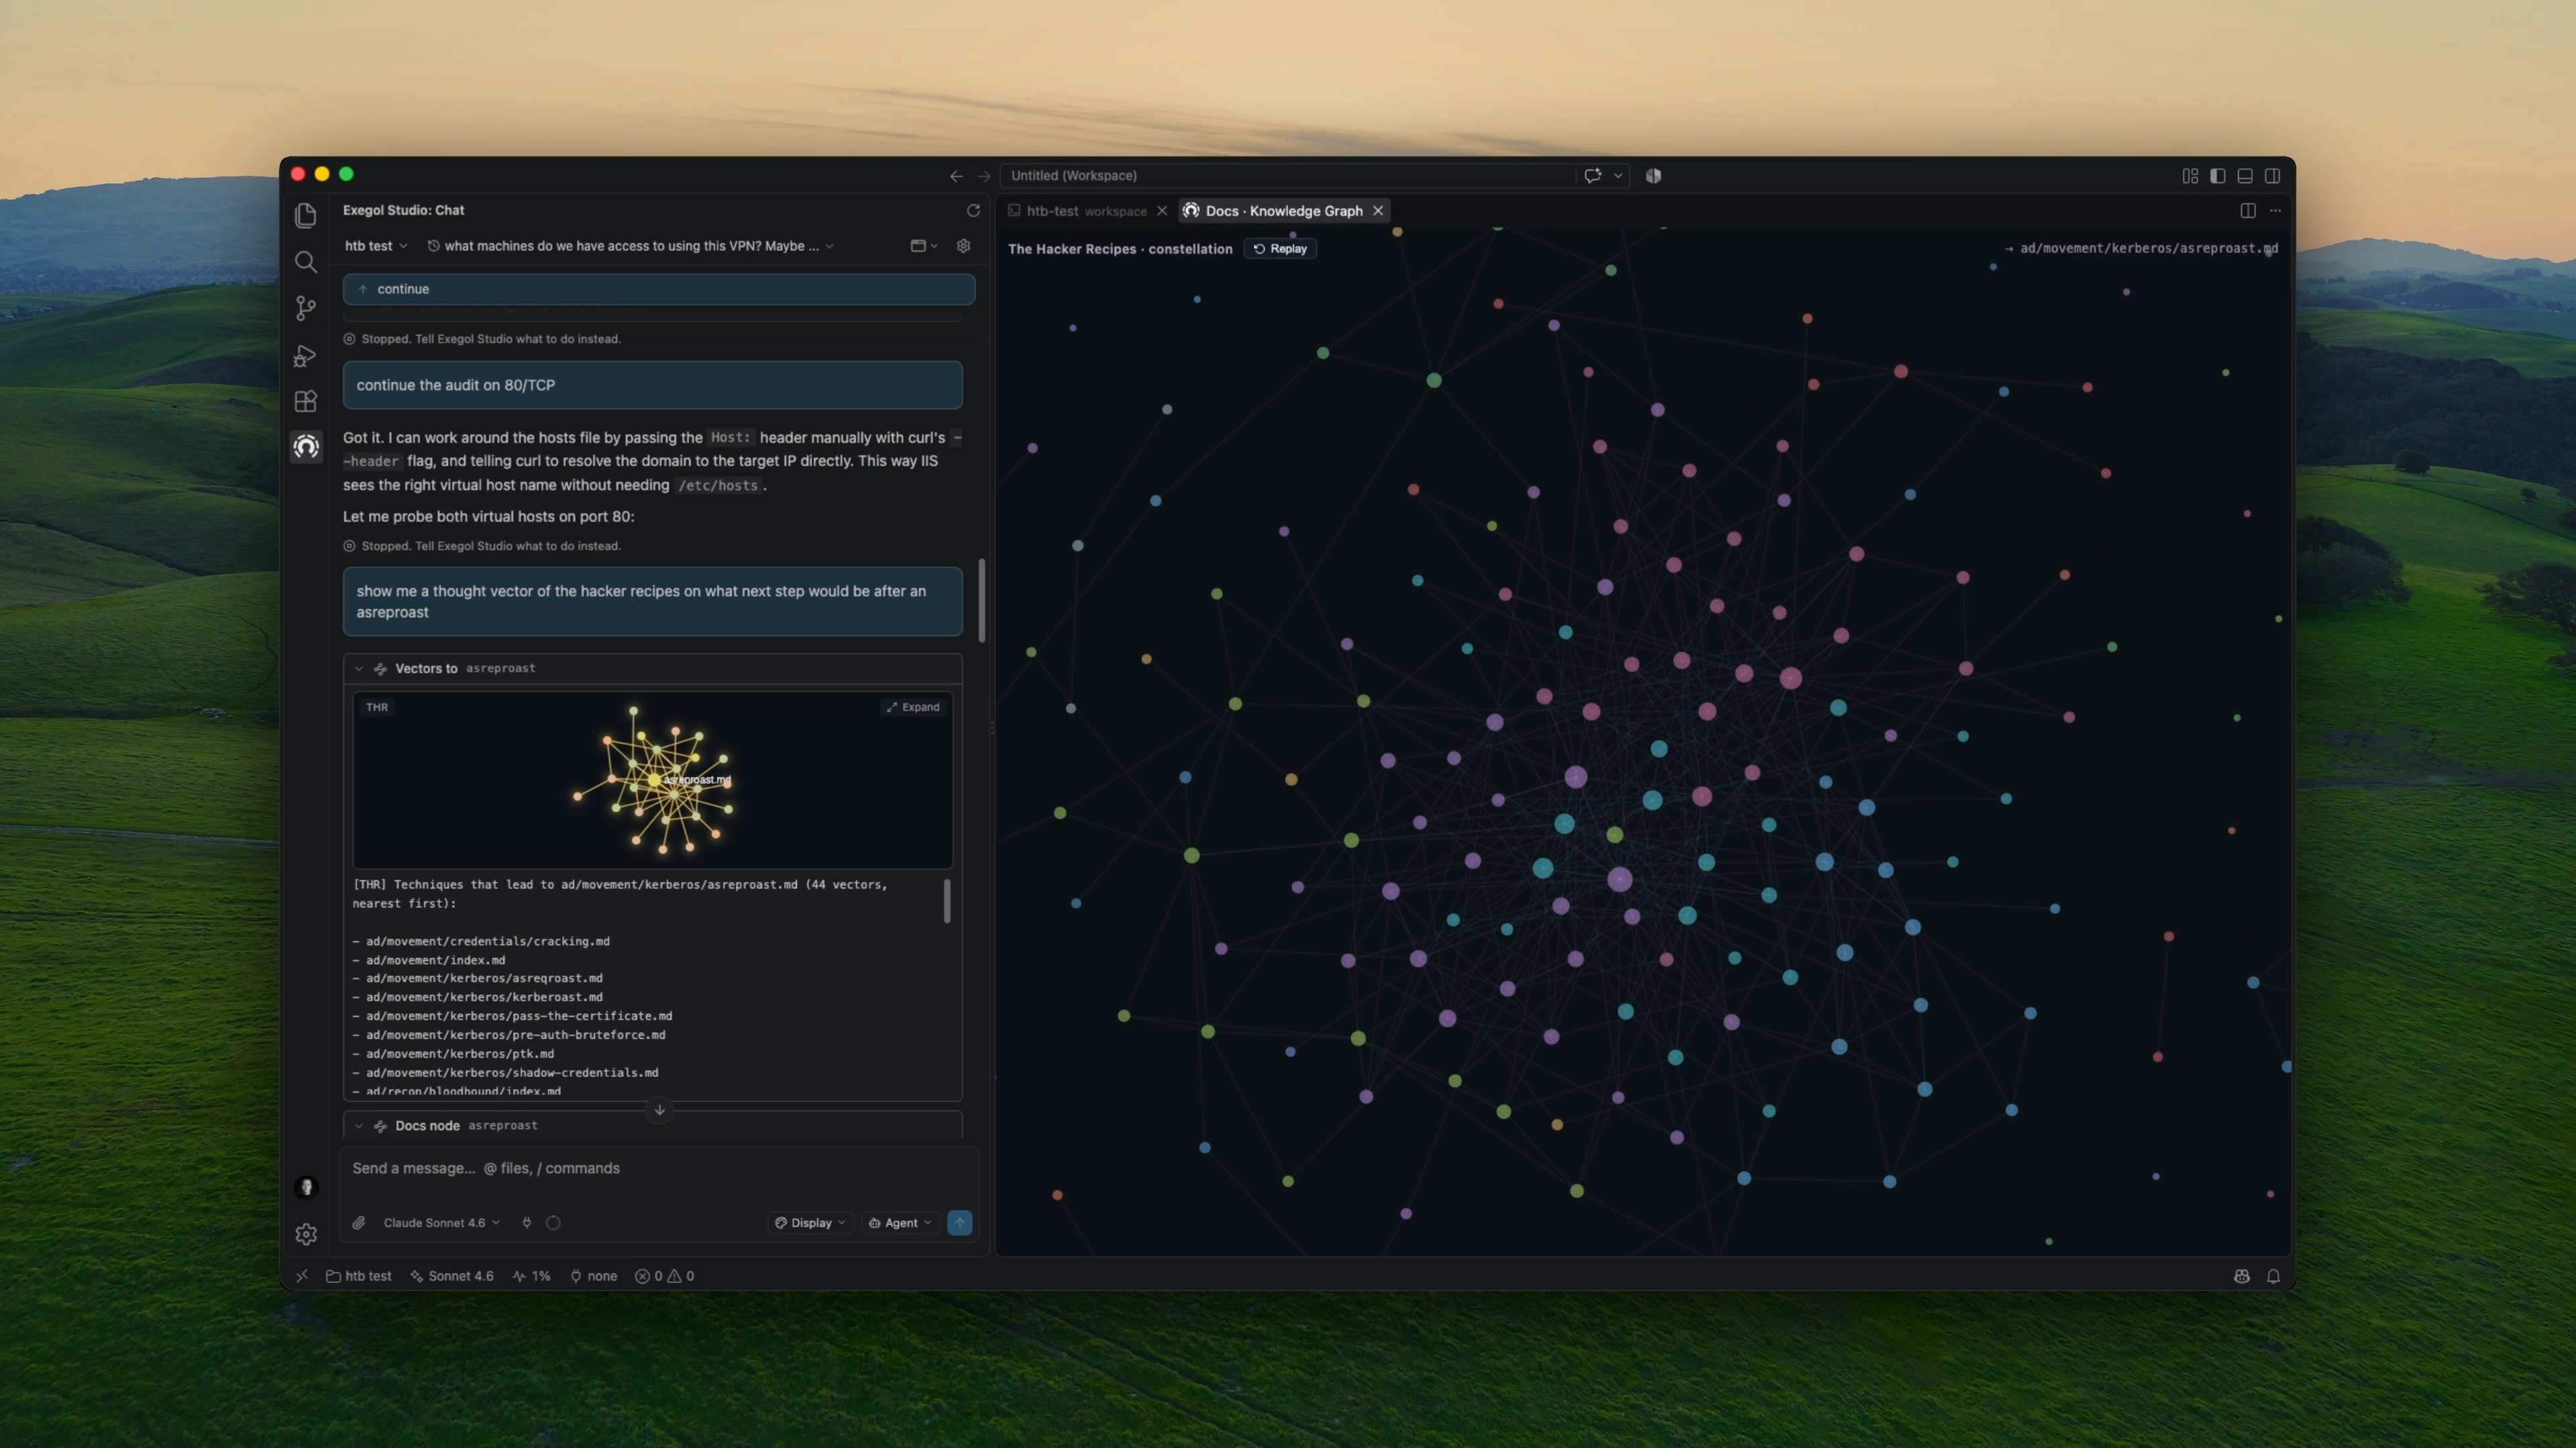
The hacker's IDE. Optional AI, under your control.
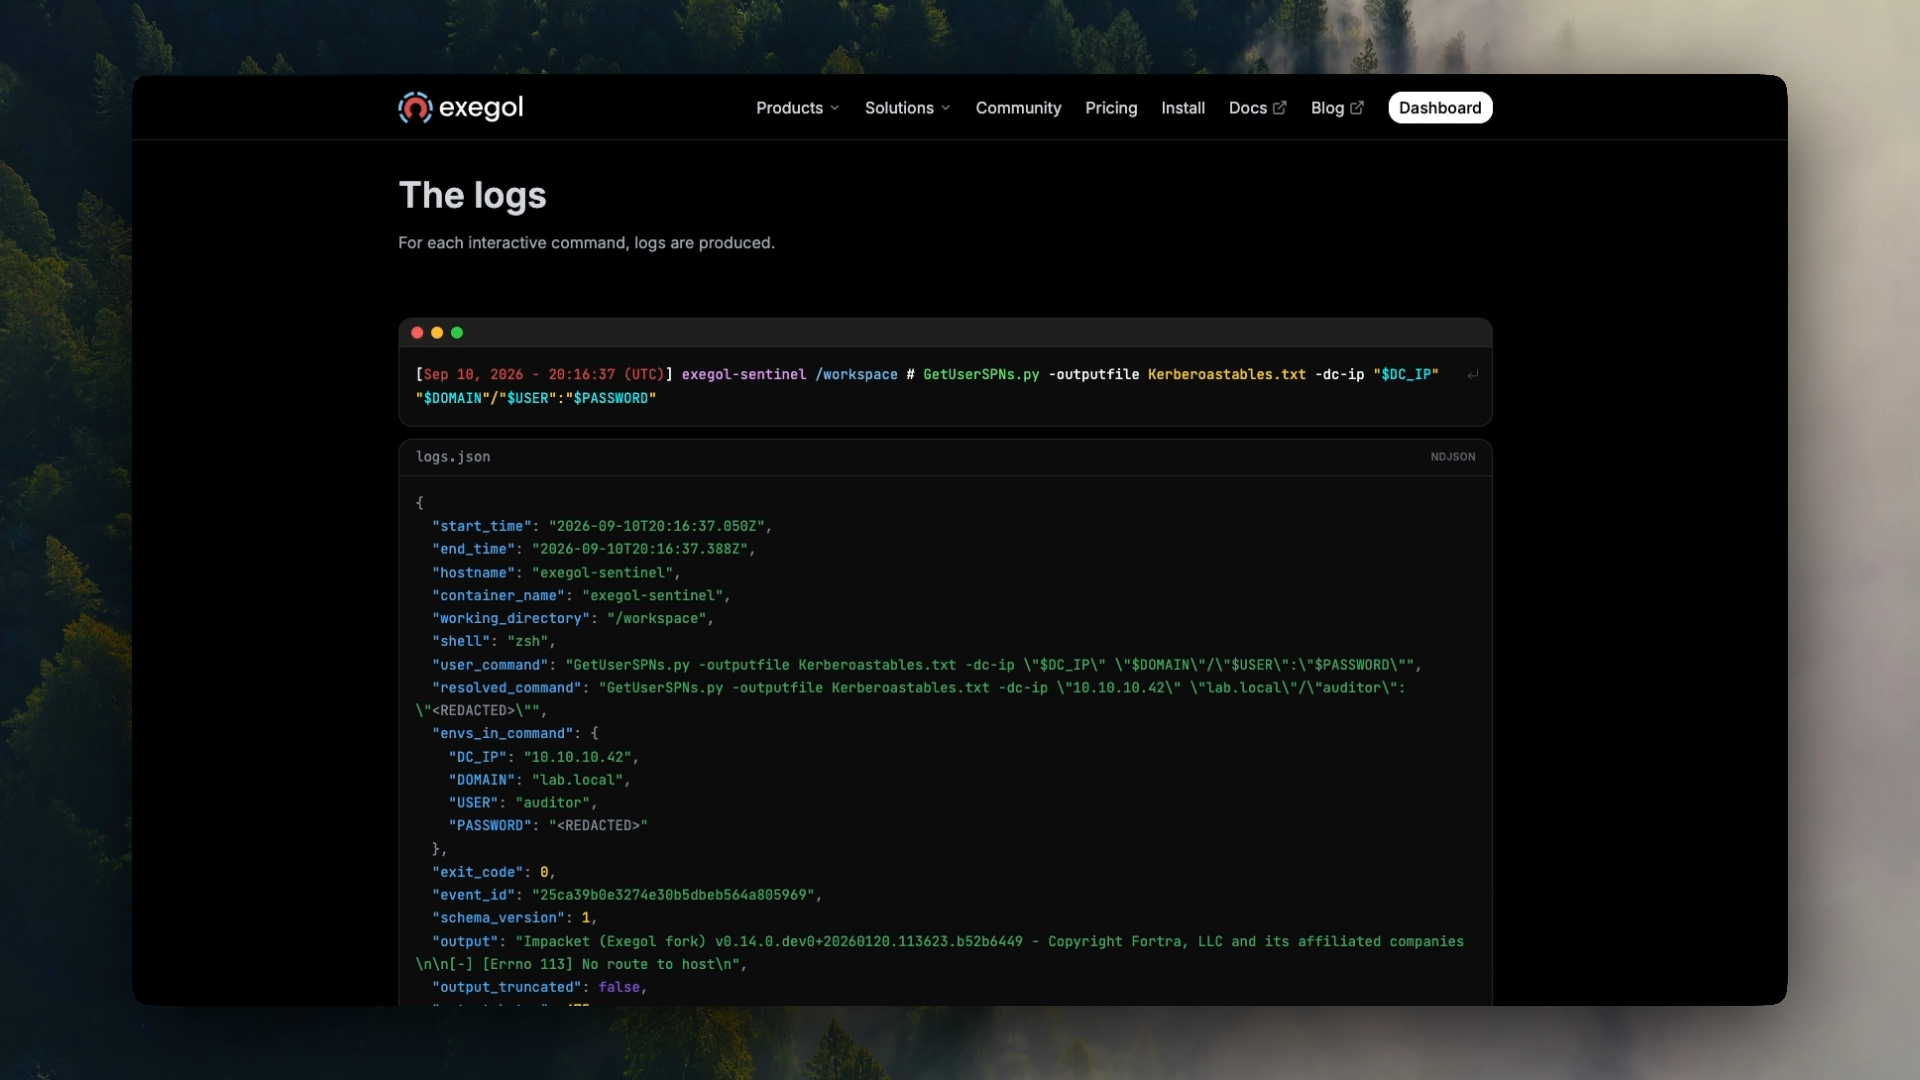
Structured command logs into your SIEM.
Let an LLM use Exegol without living on the host.
Operators need an environment that doesn't fight them. Leaders need that work to be isolated, licensed, and explainable. Exegol is built for both, on the same workstation.
You stop maintaining a distro. One container per engagement, tools already in, tunnel in the box, optional Studio and MCP when you want them.
For operatorsSame product, different job: throwable environments on machines you already own, commercial licensing, logs you can ship to a SIEM with Sentinel.
For leadersPT/RT teams, VOCs, SOCs, CERTs, pentest beneficiaries. They trust us not to disclose their names.